OpenSSH Urgently Patches Alpine Long Password Authentication Bypass Vulnerability
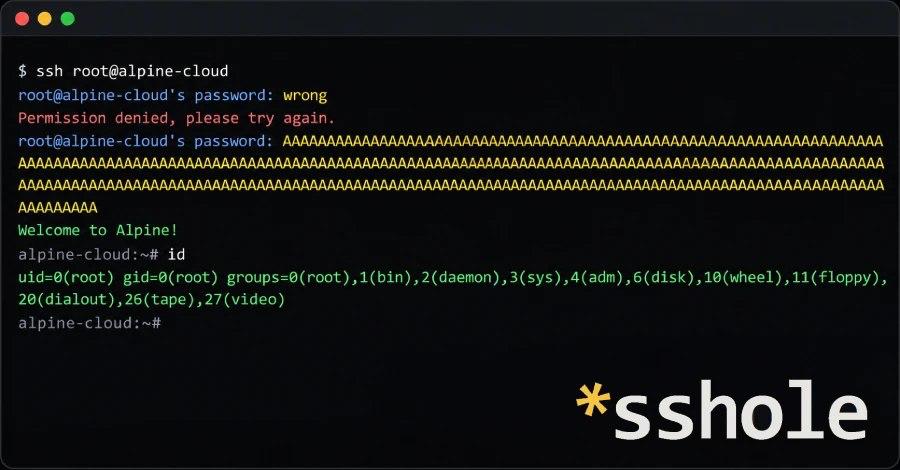
OpenSSH released 10.6p2 on November 5 to urgently fix a vulnerability allowing attackers to bypass SSH authentication using passwords of 257 to 1024 bytes. On Alpine Linux, this could enable attackers to log in to passwordless key-based accounts, provided they have network access to the server and the account name. Alpine has released patches for versions 3.16 and later. For systems unable to upgrade immediately, setting `PasswordAuthentication no` can disable password logins. No exploitation…
OpenSSH Releases Emergency Fix for Alpine Long Password Authentication Bypass Vulnerability
On November 5, OpenSSH released version 10.6p2 to urgently address a vulnerability that allowed attackers to bypass SSH authentication using passwords between 257 and 1024 bytes in length. On Alpine Linux, this flaw could have enabled attackers to log in to passwordless key-based accounts, provided they had network access to the server and knew the account name.
Alpine has already released patches for versions 3.16 and later. For systems that cannot be upgraded immediately, setting PasswordAuthentication no will disable password-based logins. No exploits have been reported so far.
Source: The Hacker News