Anker, NIKE, Freshippo, and Xianyu: Multiple Brand WeCom Accounts Post Pornographic Links Late at Night; WeCom Says Third-Party Add-ons Were Hacked
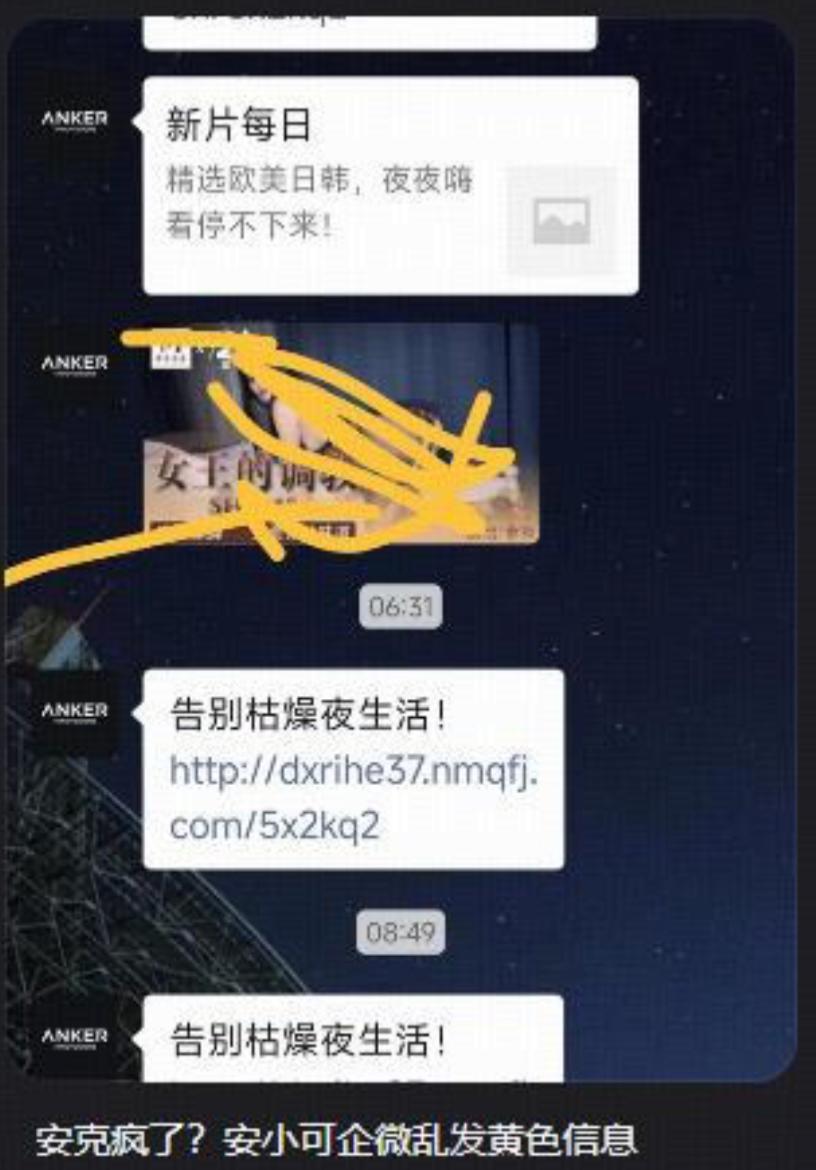
In the early hours of October 24, corporate WeChat accounts for Anker Innovations, NIKE, Freshippo, and Xianyu sent suspected sexually suggestive promotional messages and "New Film Daily" cards to user groups. WeChat Work attributed the breach to a compromised third-party plug-in, forcibly taking down the accounts and blocking the links. Anker Innovations has frozen the involved accounts and reported the incident to police, while Freshippo stated the links were not official content.
Anker, NIKE, Freshippo, and Xianyu: Multiple Brands' WeCom Customer Service Accounts Sent Pornographic Links Late at Night; WeChat Work Claims Third-Party Plugin Was Compromised
Around 5 a.m. on October 24, the WeChat Work (WeCom) customer service accounts of brands such as Anker Innovations, NIKE, Freshippo, and Xianyu sent suspected pornographic promotional messages and "New Daily Film" cards to user groups. The WeChat Work security team responded that it had confirmed a third-party plugin service was compromised, affecting accounts that used the service. The relevant accounts have been forcibly logged out, and the promotional links have been blocked.
Anker Innovations stated that it has frozen the accounts involved, reported the incident to the police, and reminded users not to click on the links. Freshippo said the links were not official content and that all parties are still investigating.
Source: ZAKER | Sina Finance