Red Hat Patches Linux Kernel TCP Remote Code Execution Flaw (9.8 CVSS)
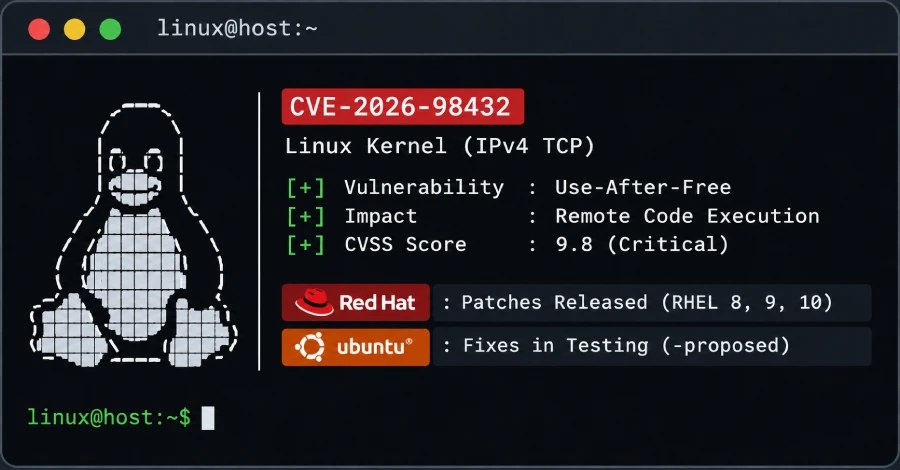
A use-after-free vulnerability, CVE-2026-98432, has been found in the Linux kernel's IPv4 TCP code. The Kernel CVE team rated it 9.8, allowing remote, unauthenticated attackers to execute code. Red Hat released a patched kernel for RHEL 8/9/10 on November 1, requiring a reboot. Fixes for Ubuntu 22.04, 24.04, and 26.04 LTS remain only in the manually enabled -proposed testing channel, with no official update date yet. No real-world exploitation has been reported.
Red Hat Patches 9.8-Rated Linux Kernel TCP Remote Code Execution Vulnerability
A use-after-free vulnerability, CVE-2026-98432, exists in the Linux kernel's IPv4 TCP code. The Kernel CVE team has rated it 9.8, allowing remote, unauthenticated attackers to execute code. Red Hat released a patched kernel for RHEL 8/9/10 on November 1, requiring a reboot.
The fix for Ubuntu 22.04, 24.04, and 26.04 LTS is still only available in the -proposed testing channel, which must be manually enabled. No official update date has been provided, and there are currently no reports of actual exploitation.
Source: The Hacker News https://thehackernews.com/2026/11/red-hat-patches-98-rated-linux-tcp-rce.html