333 Tor Exit Nodes with Backdoors Taken Offline
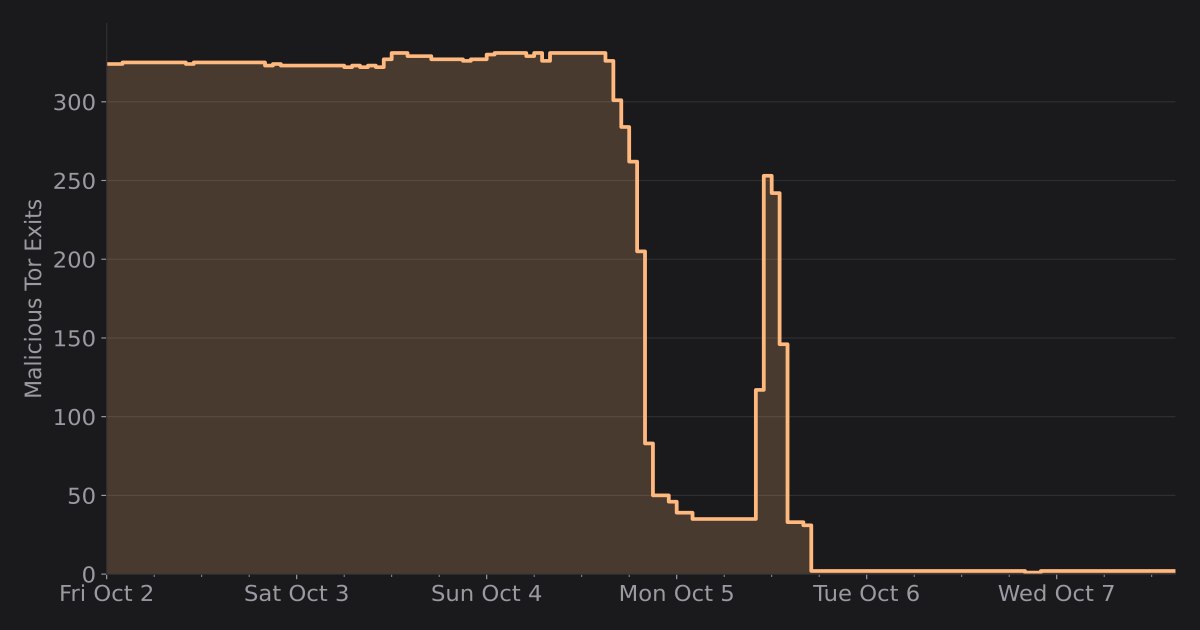
A Tor operator scanned ~3,000 exit relays and found 333 (~10%) compromised by the Ebury backdoor, enabling SSH connection hijacking on port 22 to 12 interception servers for credential theft. On October 4, these nodes were marked as BadExit and taken offline the next day. Attackers had infiltrated the servers in August, blocking specific ports to collect unencrypted email traffic; the compromise method remains unknown.
333 Tor Exit Nodes with Backdoors Taken Offline
A Tor operator used a script to scan approximately 3,000 exit relays and found that 333 of them had the Ebury backdoor implanted, accounting for about 10%. This backdoor could hijack SSH connections on port 22 to 12 interception servers and steal credentials. On October 4, these nodes were marked as BadExit, and all were taken offline the following day.
The attacker had already compromised these servers in August of this year and blocked certain ports to specifically collect unencrypted email traffic. The method of compromise remains inconclusive.
KABA
https://kaba.cx/posts/20261020_Tor/